
The secure enterprise vibe coding platform
Your business teams build production apps with AI inside your own AWS cloud. Superblocks blocks vulnerable code before it ships, keeps your data and code inside your VPC, and gives Security and IT a governed, auditable record of every app, builder, and integration.
- CVE-2026-3412 detectedUnsafe logging vulnerability discovered in axios.
- CRITICAL
- token exposure
- axios
- 1.14.1
- Fixing @corp/webhook-clientBlocking private network destinations and unsafe redirects.
- IN PROGRESS
- CVE-2026-3521
- 3.2.0 - 3.2.1
- CVE-2026-3412 detectedUnsafe logging vulnerability discovered in axios.
- VERIFIED
- PROTECTED
- 1.14.1 - 1.14.2
- @corp/image-processor securedPatched to 4.6.2 with command isolation applied.
users on one GDPR-compliant deployment
apps governed by one IT team
of the platform runs in your cloud on Cloud Prem


"When business teams can build software on their own, the question isn't whether it happens, it’s whether we can secure and govern it. Superblocks gave us an SDLC-enabled path from prototype to production, secured in our AWS VPC, with the controls to govern at scale."
The security Superblocks runs
Four controls stand between a prompt and production.
Here is each one and why it matters.
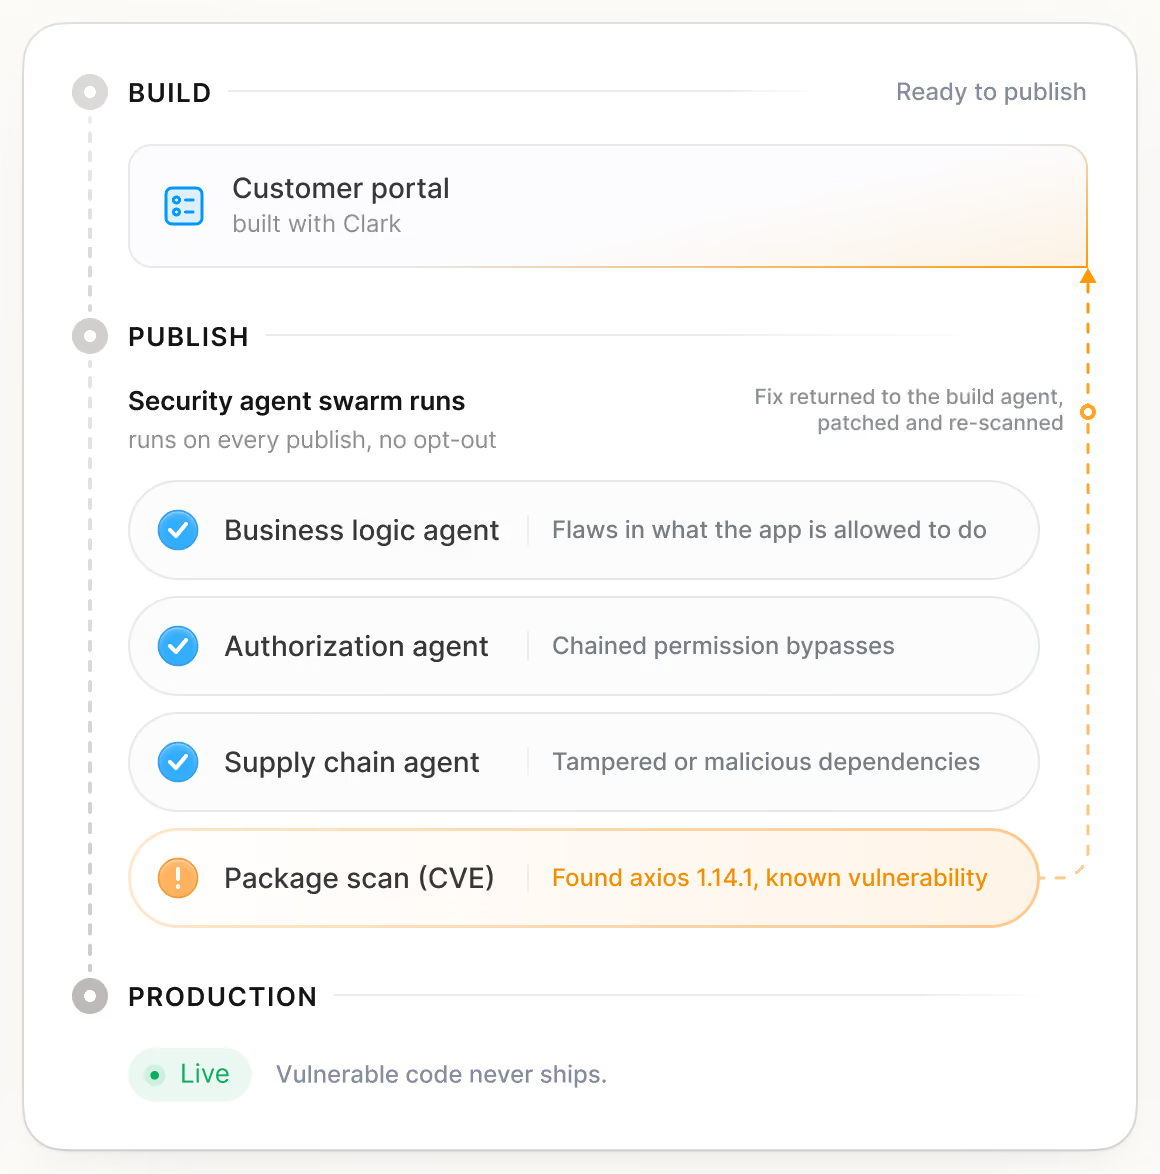
Vulnerable code doesn't ship
When publishing an app, a swarm of security agents scans every app for business logic flaws, chained authorization bypasses, and supply chain vulnerabilities. Every package is checked against CVE databases. When an agent finds a vulnerable package, it feeds the fix back to the build agent, which fixes it before deploy.
Your data never leaves your cloud
With Cloud Prem, the entire platform runs inside your cloud: control plane, data plane, and AI inference. Deploy it in your AWS account and every app inherits the network, identity, encryption, and audit controls you already run. AWS-native databases spin up with bring-your-own-key encryption, so your keys govern the data your builders create. Zero data retention on our side. Multi-region data planes handle residency by region.

Every action ties to an identity
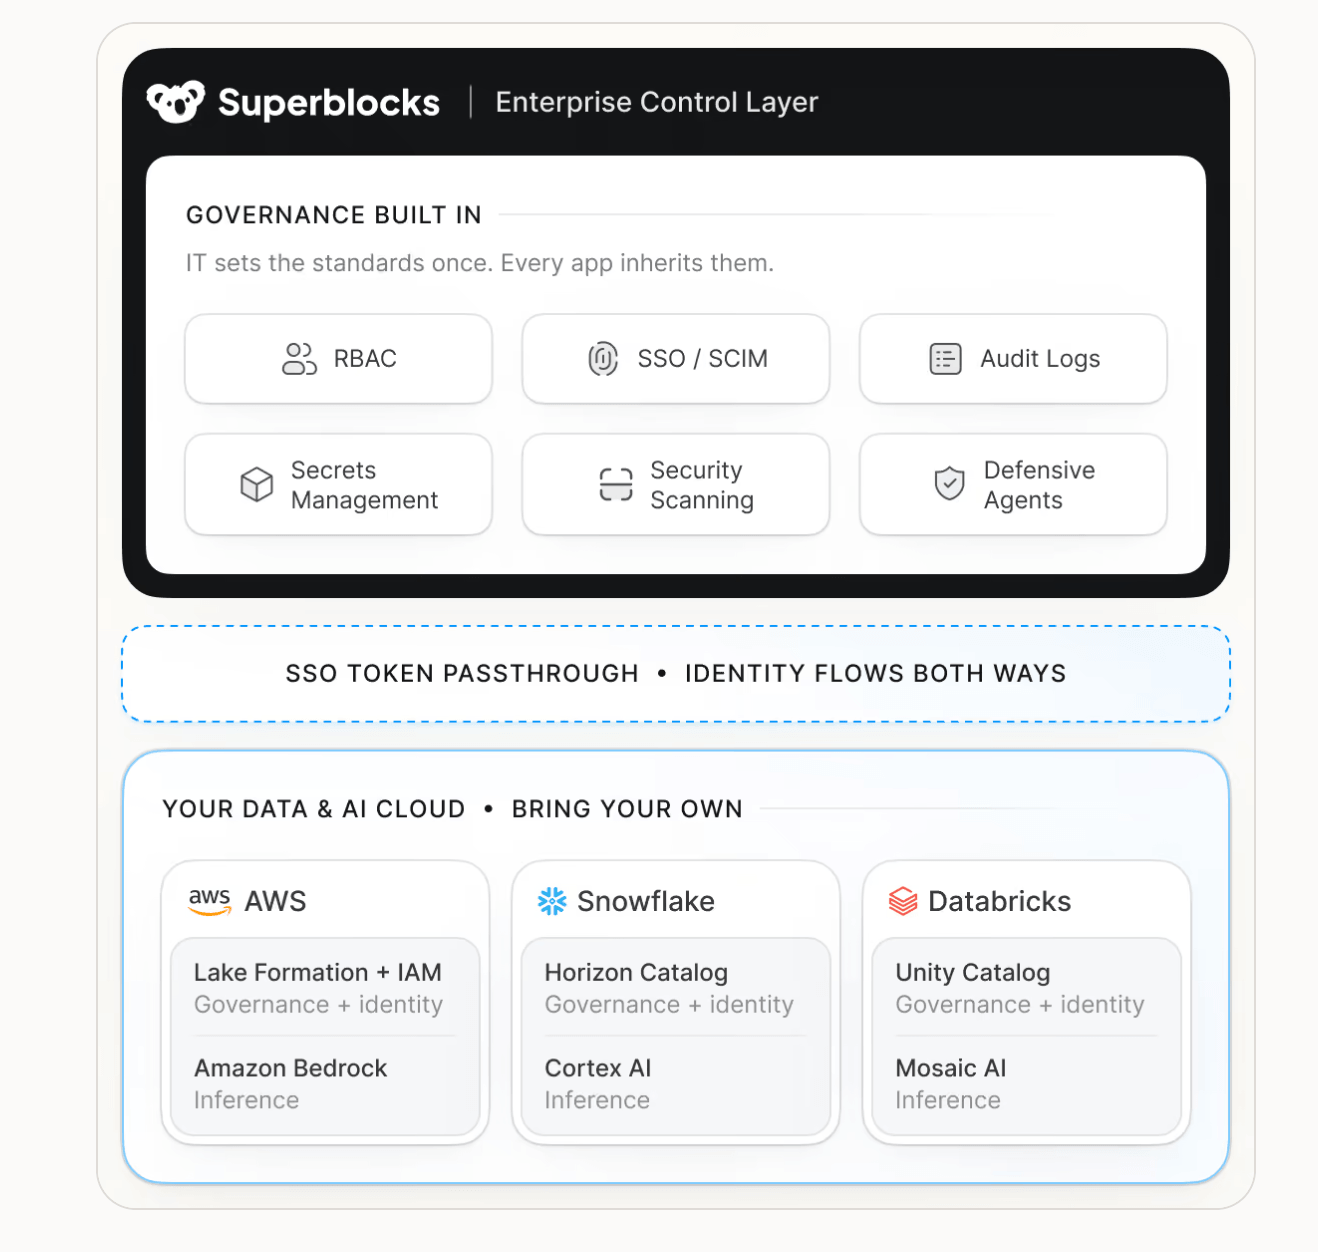
Every login federates to your identity provider through SSO. SCIM provisions and deprovisions from your directory automatically. Custom RBAC handles defaults, ABAC handles edge cases. Token pass-through means builders inherit the Snowflake, Salesforce, and database permissions they already have.
Secrets stay vaulted and referenced by name. No raw values in prompts, repos, or logs.
A software estate you can query
The Superblocks MCP turns your app estate into a system of record. Ask who built what, what data each app touches, who has access, and when it ran. Audit logs capture every build, query, integration access, and package install, retained 90+ days and exportable to your SIEM.
When the next CVE drops, you query every affected app and block deploys with one switch.

Security and IT govern every app
From build to deploy, your security tooling runs inside the pipeline and Superblocks governs what it can't see: every AI-built app, its dependencies, and its data access. Admin approval, sensitive-app gates, and per-tenant kill switches all happen between a build and production.


Choose where everything runs
Three deployment models. You pick the boundary.
| At production | Streamlit | Superblocks |  |
|---|---|---|---|
| Control plane | Superblocks cloud | Superblocks cloud | Your cloud |
| Data plane | Superblocks cloud | Your VPC | Your cloud |
| AI inference | Superblocks cloud | Superblocks cloud, non-prod data only | Your cloud |
| Data leaves your network | Outbound only, IP allowlisted | Never for production data | Never |
Most security-led companies land on Cloud Prem. Run it in your AWS account and bring your own model if policy requires it. Your data, your keys, your perimeter.
The only enterprise app platform that deploys fully in your VPC
Most SaaS tools process your data on their infrastructure. Cloud Prem is different — Superblocks runs entirely inside your AWS account. Your network. Your IAM. Your controls. Superblocks just manages the software.

Fully managed, secure and compliant. The fastest way to get started.

Superblocks manages the control plane while your data stays in your infrastructure.

The full platform runs in your cloud. Your data never leaves your VPC.
Teams run real production on Superblocks
- Tried consumer vibe coding first, then built it themselves on Superblocks: 800+ agents in production and an $850K vendor quote turned down.
- A designer with no coding background replaced Workday HR across the trust, 60 to 70 APIs and GDPR compliant.
- Quarter-long workflows collapsed to under an hour, governed end to end on their own infrastructure.
- Financial servicesShut down thousands of ungoverned vibe-coding users to standardize on Superblocks in its own cloud account.
Proof, not posture
Superblocks runs the scans inside the platform, so code never has to leave it.
- Production app serving 100,000+ users, GDPR compliant, built by a designer with zero engineering background inside IT's guardrails.
- 350+ apps across 9 departments on Cloud Prem, governed by one IT team with full audit visibility.
- Rejected an $850K vendor quote and built it internally. 800+ agents use it daily.
“That turned into a nightmare of exporting code and trying to do security scans. It didn't have the enterprise controls we were looking for.”
IT leader at a global manufacturer, on why they left Replit
As easy as Replit, more secure.
Consumer vibe coding tools optimize for "does it work." Superblocks optimizes for "does it work, and can your security team prove it's safe." Basic SOC 2 and a hosted-only architecture don't survive a real security review. Publish-time scanning, deployment in your own cloud, and a queryable audit trail do.
Questions your security team will ask
Where does our data live, and does it ever leave?
On Cloud Prem, nowhere but your cloud. Control plane, data plane, and AI inference all run in your environment, in your own AWS account. Superblocks retains nothing.
How is AI-generated code reviewed?
By something other than the AI that wrote it. A separate swarm of security agents scans at publish for business logic flaws, authorization bypasses, and supply chain vulnerabilities, and packages are checked against CVE databases. Vulnerable code gets fixed before deploy, automatically.
Do we have to replace our existing security scanners?
No. Keep your CI/CD gates and scanners. Superblocks adds the governance layer for AI-built apps: the inventory and enforcement your existing pipeline never sees.
How do access controls work?
SSO to your IdP, SCIM provisioning, custom RBAC and ABAC, and token pass-through so builders keep the data permissions they already have. Secrets are vaulted, redacted, and never appear in prompts or logs.
What happens when a CVE drops in a package our apps use?
Query the Superblocks MCP for every app running that package, block deploys platform-wide with one switch, and push the fix. Minutes, not an audit project.
How does Superblocks govern what citizen developers build?
IT sets the guardrails once: who builds, what data they reach, which integrations they use, and which standards apply to every generation. RBAC and deploy approvals enforce them on every app.
Does Superblocks address shadow AI?
Yes. Ungoverned AI-built apps are the new shadow IT. Superblocks gives builders a governed path and shows IT every app, builder, and integration in one queryable system of record, so nothing runs unseen.
Is Superblocks SOC 2 compliant?
Yes
Your teams build production apps with AI. Superblocks blocks vulnerable code before it ships, keeps your data in your private cloud, and keeps every app visible and governed.

